
Search

Search people, articles, bills, and more

CyberScoop logo

CyberScoop

cyberscoop.com

Trade PressProvenance not yet reviewed

2 stories credited to CyberScoop

Latest story Apr 22, 2026 · on ChamberLight since Apr 2026

A story can appear as several articles (copies of the same piece), so counts of stories and of articles differ.

Scores for CyberScoop

Credibility

Not enough stories yet: 1 of 10.

How this is measured

Political lean

Not enough stories yet: 1 of 10.

How this is measured

Originality

Not enough stories yet: 2 of 10.

How this is measured

Writing quality not enough rated stories yet: 1 of 10. How it is measured

Scores last checked Sep 24, 2026.

Stories ChamberLight collected, by month

Stories credited to CyberScoop, by publication date. ChamberLight collects articles that mention the officials it tracks, so this shows its own coverage of this source, not how much the source publishes.

  • Stories from CyberScoop
  • Shaded: ChamberLight collected no stories, or almost none, from any outlet (a gap in its collection, not in the outlet’s publishing)
Show as a table
MonthStoriesAll outlets
April 202624,463
May 20260none collected
June 20260none collected
July 20260none collected
August 202601 (collection gap)
September 20260598

Top topics

Share of this source’s stories tagged with each topic. A story can carry several topics, so the shares do not add up to 100%.

  • Ethics/Corruption2

    100% of 2 stories · 62% across all outlets

  • Technology/Privacy2

    100% of 2 stories · 10% across all outlets

  • Economy1

    50% of 2 stories · 26% across all outlets

  • Immigration1

    50% of 2 stories · 13% across all outlets

The thin mark on each bar is the topic’s share across all outlets.

Who they cover

Party of the officials these stories are mainly about, across all 5 officials named. A story counts once for each official it is mainly about, so the split is over 5 story–official pairs, from 2 stories.

  • Democrat60% · 3 pairs
  • Republican40% · 2 pairs

Article tone

ChamberLight’s article analysis assigns each story a tone toward the official it covers. It describes the coverage of that official, not CyberScoop’s stance, and reader votes do not change it. 2 stories.

Good Look
0 (0%)
Mixed
2 (100%)
Informational
0 (0%)
Bad Look
0 (0%)

Challenges to these scores

No one has challenged a score on this page yet. Anyone can; editors publish every outcome here.

Articles served from cyberscoop.com

5
House Republicans roll out national privacy bill

House Republicans unveiled on Wednesday Congress’ latest effort to tackle comprehensive digital privacy legislation for Americans. The Secure Data Act would allow consumers to opt out of data collection for individual businesses for the purposes of targeted advertising, selling to third parties or for use in automated decisionmaking. It would also require companies to inform consumers when their personal data is being collected or used, provide them with a portable version of that data, and give consent rights to parents over the data collection of teenagers. “This bill establishes clear, enforceable protections so that Americans remain in charge of their own data and companies are held accountable for its safe keeping,” said Brett Guthrie, R-Ky., Chair of the House Energy and Commerce Committee and Rep. John Joyce, R-Pa., who led a working charged with developing the draft legislation, in a statement. The draft bill also imposes new requirements on businesses and other organizations to limit their collection of personal consumer data to what is “adequate, relevant and reasonably necessary” and only for purposes that are disclosed to consumers in advance. They must also adopt new safeguards for customers’ personal data and disclose any third parties they share it or sell it to, including adversarial foreign governments like Russia and China. The Federal Trade Commission would be given greater oversight of data brokers that buy, collect, repackage and sell personal data to the highest bidder. The draft bill requires data brokers to register with the FTC, comply with data minimization, disclosure and data security mandates, and creates a new national data broker registry. Cobun Zwiefel-Keegan, managing director at the International Association of Privacy Professionals, told CyberScoop that based on the released draft and conversations on the Hill, the bill most resembles privacy laws passed by Virginia or Kentucky (the home state of Guthrie) in recent years, with an emphasis on providing notice and opt-out rights to individual consumers and often tying business compliance to “reasonable” standards of evidence that they acted to protect consumer data.   At the same time, Zwiefel-Keegan said it could potentially further empower the Federal Trade Commission and state Attorneys General to investigate and sanction bad actors. The bill is the product of more than 16 months of internal discussion and consensus-building within the GOP majority. While drafting it, a working group led by Rep. John Joyce (R-Pa.) and other House Republicans solicited feedback from 170 organizations and received more than 250 responses from the public to a Request for Information released last year. While they have worked to achieve consensus within their own caucus, House Republicans did not involve Democratic members in the working group or drafting process, something observers said could make it difficult to attract bipartisan support. Zwiefel-Keegan said that while the Republican drafters of the bill “would challenge Democrats to explain why they can’t support the type of bill that has been passed in blue states.” But he also noted that there are “plenty of ways that people will point to how it’s weaker than a lot of blue state privacy laws,” including federal preemption of more robust state privacy laws like those in California, the lack of a private right of action allowing individuals to sue companies directly and a mandatory 45-day “curing” period that allows companies in violation of the law to come into compliance and avoid formal sanctions.   “I think the privacy working group and the leadership of the committee thinks there’s a pretty strong chance of passing it out of committee.” After that the bill’s chances are likely dependent on other factors, like getting some Democrats on board and working with “red state representatives who may not like their own laws being preempted.” Shortly after the draft bill was released, Rep. Frank Pallone, D-N.J., ranking member on the House Energy and Commerce Committee, said he was opposed and accused House Republicans of having “lost the plot” on passing national privacy legislation. “This Republican privacy bill protects corporations and their bottom line, not people’s privacy,” Pallone said in a statement. “We should be protecting the little guy with a bill that empowers consumers, not one that preempts consumer protections at the behest of Big Tech.” Eric Null, director of the privacy and data project at the Center for Democracy and Technology, indicated that the Secure Data Act falls short, calling it full of “easily exploitable loopholes” that let companies “hide behind cookie banners and lengthy terms of service rather than establishing meaningful privacy protections.” Null was also critical of the bill’s lack of substance around AI, saying that Large Language Models pose significant privacy challenges today that will only worsen over time. “Any federal privacy law discussed in 2026 should be future-proofed by protecting against growing AI-related privacy harms, namely by limiting data collection for AI training and preventing use of the technology to discriminate against protected classes, but this bill does neither sufficiently,” he said. The American Civil Liberties Union also came out against the bill, with senior staff attorney Cody Venzke saying the GOP-led bill “places the onus on regular people” to sift through complex privacy policies created by businesses to request opt out or deletion of their data. “And it leaves us without real recourse – even blocking us from going to court – if our requests go unanswered,” said Venzke in a statement. In their joint statement, Guthrie and Joyce said they “look forward to working with our colleagues to build support for this bill and advance data privacy protections fit for our 21st century economy.” The post House Republicans roll out national privacy bill appeared first on CyberScoop.

Apr 22, 202610 votes

House Republicans roll out national privacy bill

House Republicans unveiled on Wednesday Congress’ latest effort to tackle comprehensive digital privacy legislation for Americans. The Secure Data Act would allow consumers to opt out of data collection for individual businesses for the purposes of targeted advertising, selling to third parties or for use in automated decisionmaking. It would also require companies to inform consumers when their personal data is being collected or used, provide them with a portable version of that data, and give consent rights to parents over the data collection of teenagers. “This bill establishes clear, enforceable protections so that Americans remain in charge of their own data and companies are held accountable for its safe keeping,” said Brett Guthrie, R-Ky., Chair of the House Energy and Commerce Committee and Rep. John Joyce, R-Pa., who led a working charged with developing the draft legislation, in a statement. The draft bill also imposes new requirements on businesses and other organizations to limit their collection of personal consumer data to what is “adequate, relevant and reasonably necessary” and only for purposes that are disclosed to consumers in advance. They must also adopt new safeguards for customers’ personal data and disclose any third parties they share it or sell it to, including adversarial foreign governments like Russia and China. The Federal Trade Commission would be given greater oversight of data brokers that buy, collect, repackage and sell personal data to the highest bidder. The draft bill requires data brokers to register with the FTC, comply with data minimization, disclosure and data security mandates, and creates a new national data broker registry. Cobun Zwiefel-Keegan, managing director at the International Association of Privacy Professionals, told CyberScoop that based on the released draft and conversations on the Hill, the bill most resembles privacy laws passed by Virginia or Kentucky (the home state of Guthrie) in recent years, with an emphasis on providing notice and opt-out rights to individual consumers and often tying business compliance to “reasonable” standards of evidence that they acted to protect consumer data.   At the same time, Zwiefel-Keegan said it could potentially further empower the Federal Trade Commission and state Attorneys General to investigate and sanction bad actors. The bill is the product of more than 16 months of internal discussion and consensus-building within the GOP majority. While drafting it, a working group led by Rep. John Joyce (R-Pa.) and other House Republicans solicited feedback from 170 organizations and received more than 250 responses from the public to a Request for Information released last year. While they have worked to achieve consensus within their own caucus, House Republicans did not involve Democratic members in the working group or drafting process, something observers said could make it difficult to attract bipartisan support. Zwiefel-Keegan said that while the Republican drafters of the bill “would challenge Democrats to explain why they can’t support the type of bill that has been passed in blue states.” But he also noted that there are “plenty of ways that people will point to how it’s weaker than a lot of blue state privacy laws,” including federal preemption of more robust state privacy laws like those in California, the lack of a private right of action allowing individuals to sue companies directly and a mandatory 45-day “curing” period that allows companies in violation of the law to come into compliance and avoid formal sanctions.   “I think the privacy working group and the leadership of the committee thinks there’s a pretty strong chance of passing it out of committee.” After that the bill’s chances are likely dependent on other factors, like getting some Democrats on board and working with “red state representatives who may not like their own laws being preempted.” Shortly after the draft bill was released, Rep. Frank Pallone, D-N.J., ranking member on the House Energy and Commerce Committee, said he was opposed and accused House Republicans of having “lost the plot” on passing national privacy legislation. “This Republican privacy bill protects corporations and their bottom line, not people’s privacy,” Pallone said in a statement. “We should be protecting the little guy with a bill that empowers consumers, not one that preempts consumer protections at the behest of Big Tech.” Eric Null, director of the privacy and data project at the Center for Democracy and Technology, indicated that the Secure Data Act falls short, calling it full of “easily exploitable loopholes” that let companies “hide behind cookie banners and lengthy terms of service rather than establishing meaningful privacy protections.” Null was also critical of the bill’s lack of substance around AI, saying that Large Language Models pose significant privacy challenges today that will only worsen over time. “Any federal privacy law discussed in 2026 should be future-proofed by protecting against growing AI-related privacy harms, namely by limiting data collection for AI training and preventing use of the technology to discriminate against protected classes, but this bill does neither sufficiently,” he said. The American Civil Liberties Union also came out against the bill, with senior staff attorney Cody Venzke saying the GOP-led bill “places the onus on regular people” to sift through complex privacy policies created by businesses to request opt out or deletion of their data. “And it leaves us without real recourse – even blocking us from going to court – if our requests go unanswered,” said Venzke in a statement. In their joint statement, Guthrie and Joyce said they “look forward to working with our colleagues to build support for this bill and advance data privacy protections fit for our 21st century economy.” The post House Republicans roll out national privacy bill appeared first on CyberScoop.

Apr 22, 20268 votes

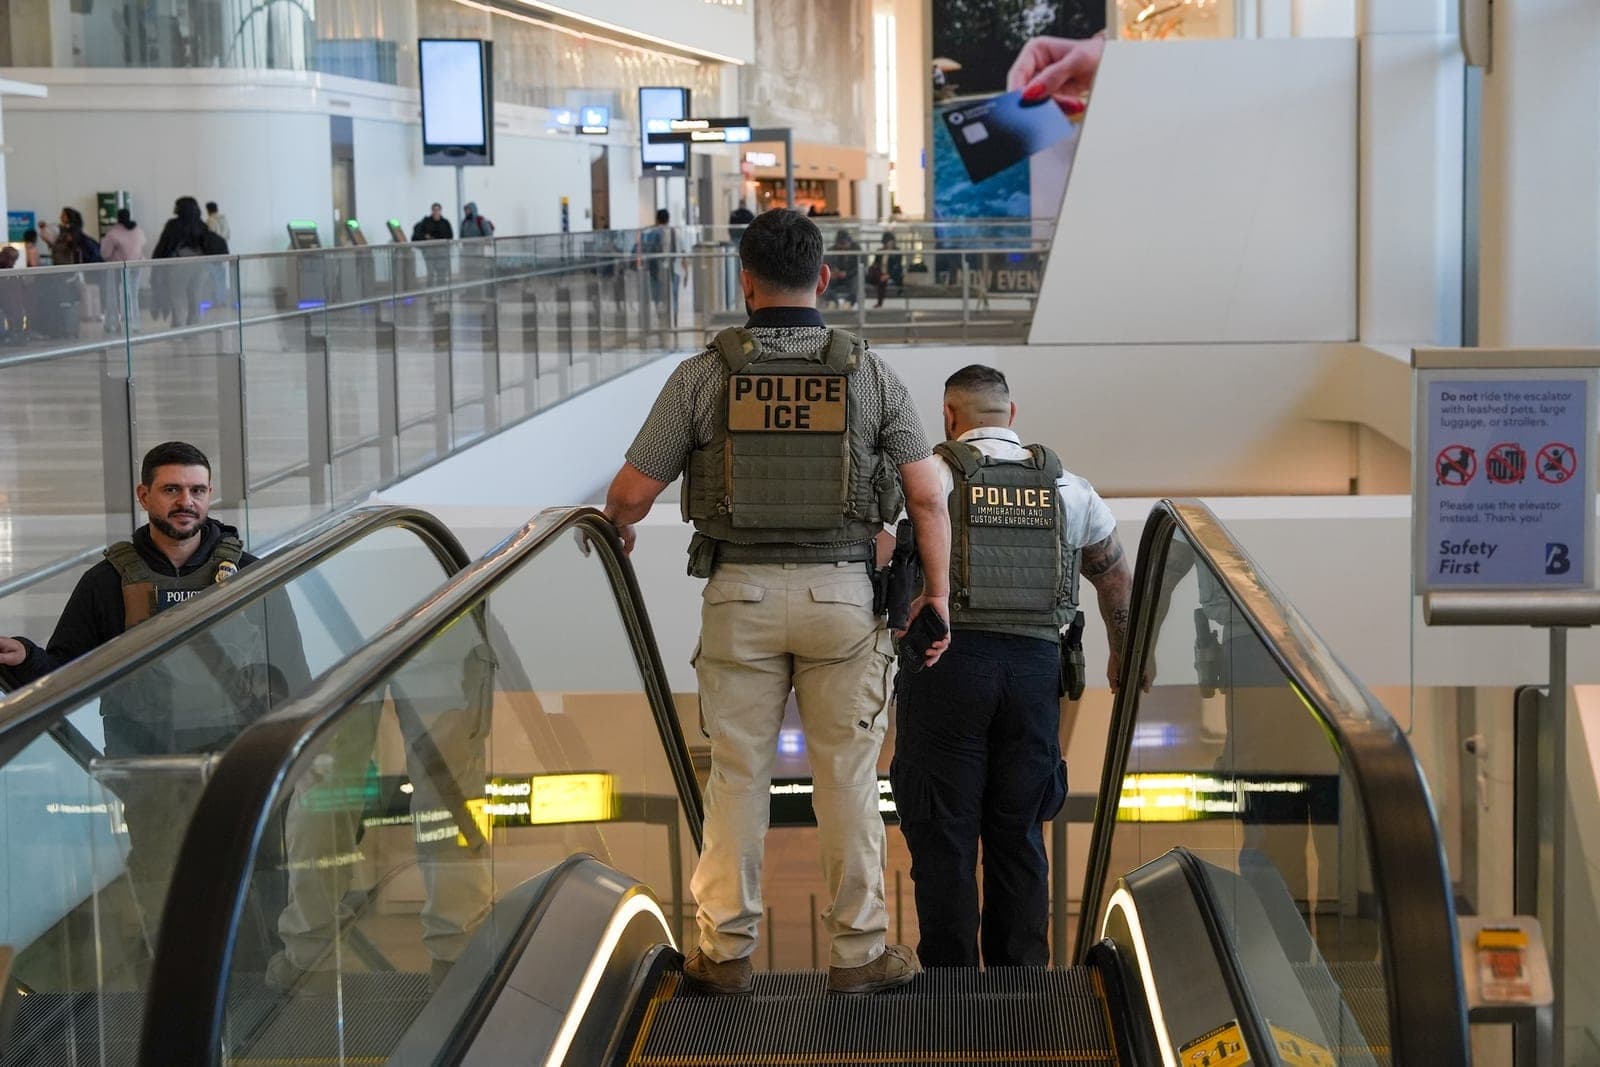
House Dems decry confirmed ICE usage of Paragon spyware

Immigration and Customs Enforcement has confirmed it is using Paragon spyware, prompting outrage Thursday from a trio of House Democrats. In response to a letter from the lawmakers inquiring about Paragon’s use, acting ICE Director Todd Lyons wrote that he had authorized the use of “cutting-edge technological tools” to help the Homeland Security Investigations division fight fentanyl, particularly against organizations using encrypted communications.  “Any use of the technology will comply with constitutional requirements and be coordinated with the ICE Office of the Principal Legal Advisor,” Lyons wrote Wednesday, without naming Paragon specifically. “Further, use of the technology will align with and support the Homeland Security Task Force’s strategic initiatives to identify, disrupt, and dismantle Foreign Terrorist Organizations, addressing the escalating fentanyl epidemic and safeguarding national security.” But Democratic Reps. Summer Lee of Pennsylvania, Shontel Brown of Ohio and Yassamin Ansari of Arizona weren’t pleased with ICE’s answer. “It’s outrageous that [the Department of Homeland Security] and ICE are using this spyware with no Congressional oversight and a complete lack of compliance standards,” they said in a joint statement shared with CyberScoop. “Given the track record of the Trump Administration, ICE’s feigned compliance with existing standards doesn’t mean much; we need to see proof and evidence of ironclad safeguards. “That’s why we requested so much documentation, which they have completely failed to provide,” they continued. “House Democrats will continue to demand more information and hold ICE accountable for its abuses.” Lyons wrote that he certified use of the technology, which he said complied with a 2023 executive order issued by then-President Joe Biden. That executive order requires certification that use of commercial spyware wouldn’t pose national security or counterintelligence risks, or create significant risks of improper use by a foreign government. In 2024, the $2 million ICE contract with Paragon came under White House review. But last year, ICE lifted a stop-work order. ICE didn’t immediately respond to a request for comment on the Democrats’ reaction. ICE’s use of surveillance technology has drawn concern from civil liberties groups. Paragon’s Graphite technology has been found on the phones of journalists and there are suspected uses in a number of countries. WhatsApp last year said it had disrupted a campaign employing the spyware against its users. The letter’s vague language on safeguards, combined with ICE’s stance on privacy, is concerning, said Cooper Quintin, a security researcher and senior public interest technologist with the Electronic Frontier Foundation’s Threat Lab. “It leaves open the door for them to interpret that it is constitutional for them to use administrative subpoenas to use this malware in HSI investigations,” Quintin said. Bloomberg first reported on Lyons’ letter. This story was updated April 2, 2026, with comments from Quintin. The post House Dems decry confirmed ICE usage of Paragon spyware appeared first on CyberScoop.

Apr 2, 20267 votes

House Dems decry confirmed ICE usage of Paragon spyware

Immigration and Customs Enforcement has confirmed it is using Paragon spyware, prompting outrage Thursday from a trio of House Democrats. In response to a letter from the lawmakers inquiring about Paragon’s use, acting ICE Director Todd Lyons wrote that he had authorized the use of “cutting-edge technological tools” to help the Homeland Security Investigations division fight fentanyl, particularly against organizations using encrypted communications.  “Any use of the technology will comply with constitutional requirements and be coordinated with the ICE Office of the Principal Legal Advisor,” Lyons wrote Wednesday, without naming Paragon specifically. “Further, use of the technology will align with and support the Homeland Security Task Force’s strategic initiatives to identify, disrupt, and dismantle Foreign Terrorist Organizations, addressing the escalating fentanyl epidemic and safeguarding national security.” But Democratic Reps. Summer Lee of Pennsylvania, Shontel Brown of Ohio and Yassamin Ansari of Arizona weren’t pleased with ICE’s answer. “It’s outrageous that [the Department of Homeland Security] and ICE are using this spyware with no Congressional oversight and a complete lack of compliance standards,” they said in a joint statement shared with CyberScoop. “Given the track record of the Trump Administration, ICE’s feigned compliance with existing standards doesn’t mean much; we need to see proof and evidence of ironclad safeguards. “That’s why we requested so much documentation, which they have completely failed to provide,” they continued. “House Democrats will continue to demand more information and hold ICE accountable for its abuses.” Lyons wrote that he certified use of the technology, which he said complied with a 2023 executive order issued by then-President Joe Biden. That executive order requires certification that use of commercial spyware wouldn’t pose national security or counterintelligence risks, or create significant risks of improper use by a foreign government. In 2024, the $2 million ICE contract with Paragon came under White House review. But last year, ICE lifted a stop-work order. ICE didn’t immediately respond to a request for comment on the Democrats’ reaction. ICE’s use of surveillance technology has drawn concern from civil liberties groups. Paragon’s Graphite technology has been found on the phones of journalists and there are suspected uses in a number of countries. WhatsApp last year said it had disrupted a campaign employing the spyware against its users. The letter’s vague language on safeguards, combined with ICE’s stance on privacy, is concerning, said Cooper Quintin, a security researcher and senior public interest technologist with the Electronic Frontier Foundation’s Threat Lab. “It leaves open the door for them to interpret that it is constitutional for them to use administrative subpoenas to use this malware in HSI investigations,” Quintin said. Bloomberg first reported on Lyons’ letter. This story was updated April 2, 2026, with comments from Quintin. The post House Dems decry confirmed ICE usage of Paragon spyware appeared first on CyberScoop.

Apr 2, 202614 votes

House Dems decry confirmed ICE usage of Paragon spyware

Immigration and Customs Enforcement has confirmed it is using Paragon spyware, prompting outrage Thursday from a trio of House Democrats. In response to a letter from the lawmakers inquiring about Paragon’s use, acting ICE Director Todd Lyons wrote that he had authorized the use of “cutting-edge technological tools” to help the Homeland Security Investigations division fight fentanyl, particularly against organizations using encrypted communications.  “Any use of the technology will comply with constitutional requirements and be coordinated with the ICE Office of the Principal Legal Advisor,” Lyons wrote Wednesday, without naming Paragon specifically. “Further, use of the technology will align with and support the Homeland Security Task Force’s strategic initiatives to identify, disrupt, and dismantle Foreign Terrorist Organizations, addressing the escalating fentanyl epidemic and safeguarding national security.” But Democratic Reps. Summer Lee of Pennsylvania, Shontel Brown of Ohio and Yassamin Ansari of Arizona weren’t pleased with ICE’s answer. “It’s outrageous that [the Department of Homeland Security] and ICE are using this spyware with no Congressional oversight and a complete lack of compliance standards,” they said in a joint statement shared with CyberScoop. “Given the track record of the Trump Administration, ICE’s feigned compliance with existing standards doesn’t mean much; we need to see proof and evidence of ironclad safeguards. “That’s why we requested so much documentation, which they have completely failed to provide,” they continued. “House Democrats will continue to demand more information and hold ICE accountable for its abuses.” Lyons wrote that he certified use of the technology, which he said complied with a 2023 executive order issued by then-President Joe Biden. That executive order requires certification that use of commercial spyware wouldn’t pose national security or counterintelligence risks, or create significant risks of improper use by a foreign government. In 2024, the $2 million ICE contract with Paragon came under White House review. But last year, ICE lifted a stop-work order. ICE didn’t immediately respond to a request for comment on the Democrats’ reaction. ICE’s use of surveillance technology has drawn concern from civil liberties groups. Paragon’s Graphite technology has been found on the phones of journalists and there are suspected uses in a number of countries. WhatsApp last year said it had disrupted a campaign employing the spyware against its users. The letter’s vague language on safeguards, combined with ICE’s stance on privacy, is concerning, said Cooper Quintin, a security researcher and senior public interest technologist with the Electronic Frontier Foundation’s Threat Lab. “It leaves open the door for them to interpret that it is constitutional for them to use administrative subpoenas to use this malware in HSI investigations,” Quintin said. Bloomberg first reported on Lyons’ letter. This story was updated April 2, 2026, with comments from Quintin. The post House Dems decry confirmed ICE usage of Paragon spyware appeared first on CyberScoop.

Apr 2, 202612 votes